Binance Says 90% of $6.3 Billion Stolen in Record Hack Is Covered as FBI Blames North Korea

Binance, the world’s largest cryptocurrency exchange, said on Saturday that it has already covered 90 per cent of the roughly $6.3 billion stolen in the largest cryptocurrency theft on record, buying replacement tokens with its own money as the FBI formally blamed North Korea for the attack. The exchange said it remained on track to reopen customer withdrawals on Sunday, three days after the breach froze billions of dollars of user funds and shook confidence across the digital-asset industry.
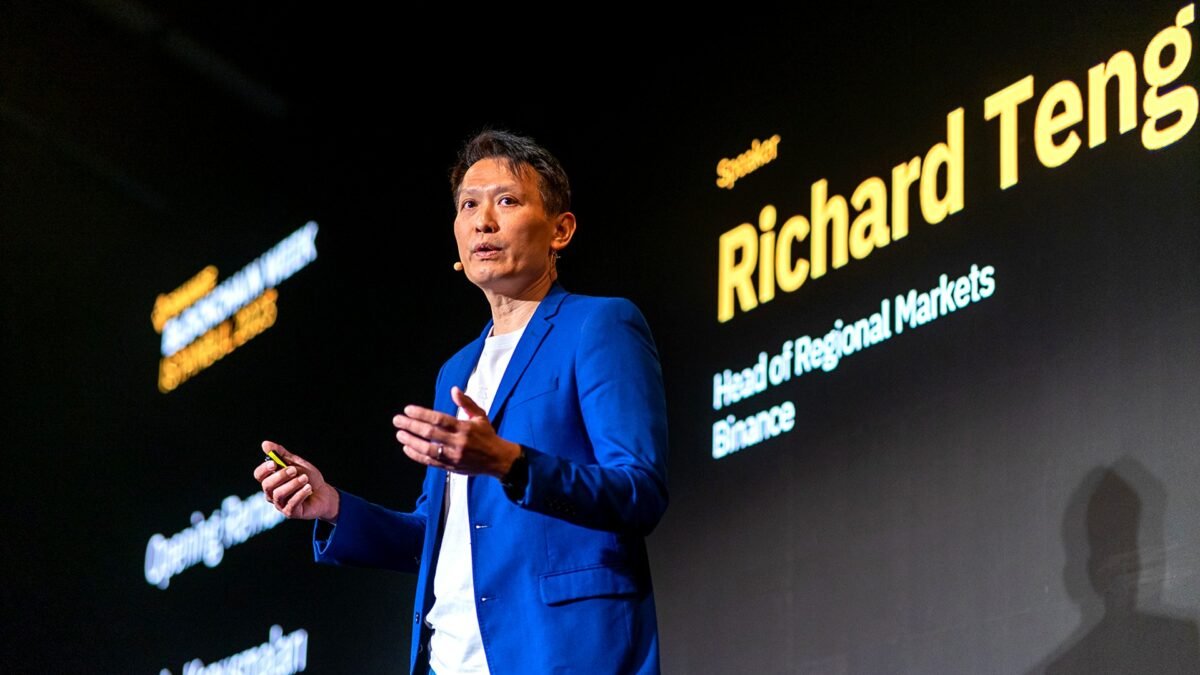
Binance said it had set aside more than $6.34 billion of company funds to make users whole, and that the remaining 10 per cent of the stolen assets consisted of less liquid tokens that would take longer to buy back through markets and over-the-counter deals. “We’ve now replenished 90% of the stolen assets, and we’re committed to covering the remaining 10%. Our users will not bear the financial impact of this incident,” co-chief executive Richard Teng said on X on Saturday, according to Reuters.
The money used to buy back the tokens came from three sources, Binance said: its corporate treasury, part of its $1 billion Secure Asset Fund for Users, known as SAFU, and some of its Futures Insurance Fund. Ten major cryptocurrencies — bitcoin, ether, Tether, Binance Coin, Solana, USD Coin, XRP, World Liberty Financial USD, Ripple USD and Zcash — are now fully backed at 100 per cent, the company said.
The announcement capped a frantic 48 hours for the exchange. On Thursday, about $6.3 billion worth of cryptocurrency drained out of Binance’s internet-connected hot wallets in roughly 20 minutes, according to blockchain analytics firm TRM Labs, which estimated the total at about $6.36 billion across ten blockchains. Binance immediately paused deposits and withdrawals, and on Friday said about $3 billion of the stolen assets had been frozen on-chain with the help of law enforcement, token issuers and other industry partners.
On Saturday, the FBI said North Korea was responsible. In a public statement, the bureau said the state-sponsored hacking unit known as TraderTraitor carried out the attack on or about 29 October, and that investigators had observed the hackers converting the stolen cryptocurrency primarily into ether, the native token of the Ethereum network, which can be moved quickly through decentralised finance services. The FBI said it expected “further laundering” of the assets and published a lengthy list of cryptocurrency addresses it said had held stolen funds or were associated with the North Korean operation. It is working with the US Secret Service and the Internal Revenue Service’s criminal investigation division to trace the money and disrupt the laundering operation.
TraderTraitor is the same North Korean unit the FBI blamed for the $1.5 billion theft from the Bybit exchange in February 2025, which until this week was the largest cryptocurrency heist ever recorded. Blockchain firms TRM Labs and Chainalysis had also attributed the Binance attack to TraderTraitor with high confidence before the FBI’s announcement, pointing to the speed of the theft, the laundering patterns and the infrastructure used.
Binance said the breach involved several “points of breach”, including a software engineer’s laptop, and that the attackers used malicious software designed to delete evidence of their activity, making the theft harder to trace and investigate. Teng described the attack as “complex” in a statement on Friday, according to Reuters. The company has not said how the attackers first gained access to the laptop or how they moved from there into the systems controlling the hot wallets.
Cryptocurrency prices fell on Friday as the scale of the theft became clear, and the incident dominated discussion across the industry over the weekend. Binance sought to steady nerves by publishing a new snapshot of the assets held on its platform, taken at midnight Coordinated Universal Time on Saturday, as part of its proof-of-reserves process. It said a full zero-knowledge proof, allowing users to independently verify that their holdings are backed at least one-to-one, was expected by Tuesday 3 November.
President Donald Trump, asked on Friday whether North Korea was involved, told reporters that US officials were “looking at that”, and pointed to Binance’s assurances about recovering the money. “Well, they say they’re gonna get it back, and they’re guaranteeing it or something. They are,” he said, according to reports of his remarks. The Secret Service said its investigators were “working around the clock with our private-sector partners, including Circle, to identify, freeze, trace and recover funds stolen from Binance”, and that it was coordinating with the US Attorney’s Office for the District of Columbia.
The speed of Binance’s response — a public pledge to absorb the loss within a day, followed by a 90 per cent replenishment figure within two — stands in sharp contrast to the history of exchange hacks, where customers have often waited years for partial recoveries, or received nothing at all. Whether withdrawals resume smoothly on Sunday, as promised, will be the first real test of that pledge.
How the biggest crypto theft in history unfolded
The attack began on Thursday 29 October, when about $6.3 billion in cryptocurrency moved out of Binance’s hot wallets — the internet-connected wallets an exchange uses to process day-to-day withdrawals — in the space of about 20 minutes. TRM Labs, which tracks illicit cryptocurrency flows, put the figure at about $6.36 billion spread across ten blockchains, with most of the value moved in a single burst of transactions.
Hot wallets are the soft underbelly of every centralised exchange. Unlike cold wallets, which are kept offline and require human authorisation to move funds, hot wallets are connected to the internet so that customers can withdraw at any time. Exchanges normally keep only a small fraction of their holdings in hot wallets for that reason. The scale of this theft suggests the attackers gained access to systems that controlled far more than a routine operational float — a point investigators and the industry will be pressing Binance to explain in the days ahead.
Binance said on Friday that it had detected several points of breach, including one software engineer’s laptop, and that the attackers deployed malicious software designed to delete evidence of their activity. That detail matters: it suggests a deliberate, patient intrusion rather than a smash-and-grab exploit of a single software bug. North Korean hacking units, according to US and South Korean intelligence assessments reported over several years, routinely spend months inside a target’s networks, studying its internal controls and waiting for the right moment before striking — a pattern consistent with what Binance has described so far.
Within hours of the theft, Binance paused all deposits and withdrawals, a standard emergency step that prevents further losses but strands customers’ money. On Friday it said roughly $3 billion of the stolen assets had been frozen, thanks to cooperation with law enforcement, token issuers — who can in some cases freeze or blacklist tokens at the smart-contract level — and other exchanges and blockchain firms that flagged the tainted funds. Freezing is not the same as recovering: the assets remain in the attackers’ wallets, but they cannot easily be spent or converted through legitimate channels.
The remaining question is how much of the stolen money the attackers managed to convert into ether and move through decentralised services before the freeze took hold. The FBI said it had observed the hackers converting stolen assets primarily into ether, and warned of further laundering. Ether is a favoured destination for crypto thieves because it can be swapped, mixed and bridged across chains through decentralised protocols that have no central operator to freeze an account — a cat-and-mouse game that has played out after almost every major North Korean theft.
What “90 per cent covered” actually means
The figure Binance announced on Saturday needs careful reading, because it is not the same as recovering 90 per cent of the stolen money. What Binance has done is buy replacement tokens with its own funds and credit them against the shortfall, so that customer balances are backed again. The stolen tokens themselves are, for the most part, still in the hands of the attackers or frozen in wallets the attackers control.
That distinction matters for two reasons. First, it means Binance, not its users, is absorbing a loss of more than $6 billion — one of the largest single corporate losses in the history of the crypto industry. Second, it means the exchange’s ability to keep its promise depends on its own balance sheet and on the liquidity of the tokens it still needs to buy. The company said the remaining 10 per cent consists of less liquid tokens, which may take longer to acquire through markets and over-the-counter deals without pushing prices against itself.
The three funding sources Binance named tell their own story. The Secure Asset Fund for Users, or SAFU, was created by Binance in 2018 as an emergency insurance fund, seeded with 10 per cent of trading fees, to protect users in exactly this kind of event. Its use now is the fund’s biggest test. The Futures Insurance Fund performs a similar backstop role for the exchange’s derivatives business. The corporate treasury is the remainder — Binance’s own cash and crypto reserves. The company has not said how much each source contributed, or what the replenishment cost it in total, and the tokens it bought back may have been purchased at prices different from those at the time of the theft.
For users, the practical question is simpler: can they get their money out? Binance said on Saturday that it was still on track to reopen withdrawals on Sunday, subject to security checks and final confirmation. A smooth reopening would be a powerful demonstration that the exchange’s balance sheet can absorb a blow of this size. A delay, a partial reopening, or withdrawal limits would revive the doubts that have dogged centralised exchanges since the collapse of FTX in 2022, when customers discovered that their funds had not been held as promised.
Binance also published a fresh proof-of-reserves snapshot, taken at 00:00 UTC on Saturday, and said a full zero-knowledge proof would follow by Tuesday 3 November, allowing holders of the ten listed tokens to verify independently that their assets are backed at least one-to-one. Proof of reserves has become the industry’s standard answer to the trust question since the FTX collapse, but it has limits: it shows what an exchange holds at a single moment, not how it manages risk day to day, and it depends on users actually checking it.
Analysis: Why It Matters
A $6.3 billion stress test of the “too big to fail” exchange
The most important fact in this story is not the size of the theft but the speed and scale of the response. A $6.3 billion loss would have destroyed almost any other exchange in the industry. Binance absorbed it in two days and kept operating. That is a statement about the sheer scale of the company’s balance sheet — and about how concentrated the crypto industry has become. The world’s largest exchange is now so large that it can swallow a loss bigger than the entire market capitalisation of most of its competitors. That concentration is both a strength and a vulnerability: it means one company’s security practices are now a matter of systemic importance for the whole market, in much the same way a major bank’s solvency is. Regulators who have spent years arguing about whether crypto exchanges should face bank-like rules will find fresh ammunition here — and so will those who argue that the market needs them.
North Korea’s crypto playbook, now at industrial scale
The FBI’s attribution to TraderTraitor, if confirmed by further evidence, would make this the biggest single North Korean cyber theft ever recorded — roughly four times the size of the Bybit heist in February 2025, which itself was then the record. United Nations sanctions monitors have previously said that North Korean cyber thefts help fund the country’s weapons programmes, and the sums involved have grown steadily as the regime’s hackers have become more sophisticated. The pattern is now well established: months of quiet infiltration, a lightning-fast theft measured in minutes, conversion into ether, and laundering through decentralised services that are hard to police. Each successful theft finances the next operation. The Binance attack suggests the playbook has not been disrupted by the international attention paid to Bybit — if anything, it has been scaled up. That raises uncomfortable questions about whether the industry’s defences are improving at all, or whether attackers are simply outpacing them.
Trust is the real currency — and it is fragile
Cryptocurrency prices fell on Friday as the news spread, a reminder that the market’s confidence rests on a fragile foundation: the belief that the places holding people’s money are safe. Binance’s rapid pledge to cover the loss was designed to shore up that belief, and the 90 per cent figure was chosen to show momentum. But trust in crypto is not restored by press statements; it is restored by withdrawals working. Sunday’s reopening is therefore the most important moment in this story so far. If customers can withdraw freely, the episode will be remembered as a remarkable demonstration of resilience. If they cannot, or if limits appear, the damage to confidence could spread far beyond Binance, because every other exchange will face the same question from its customers: could this happen to you, and could you afford it?
The laptop in the middle of a $6.3 billion heist
The detail that the breach involved a software engineer’s laptop is the most revealing — and the most worrying — fact Binance has disclosed. The largest theft in crypto history did not begin with a sophisticated attack on a blockchain protocol or a flaw in a smart contract. It began, apparently, with a single employee’s device. That is a human and organisational failure, not a technological one, and it is the hardest kind to fix: it requires training, access controls, device management and a culture in which security is treated as everyone’s job. The industry has spent billions on cryptography and very little, relatively speaking, on the unglamorous work of keeping its own people safe from phishing, social engineering and malware. Until that changes, the next record-breaking theft is a matter of time, not chance.
Regulators will not let this pass quietly
A $6.3 billion theft from the world’s largest exchange, attributed to a sanctioned state actor, is the kind of event that accelerates regulation. In the United States, where the Trump administration has taken a markedly friendlier approach to crypto than its predecessor, the political dynamics are complicated: the president himself commented on the hack, and his administration’s instinct has been to support the industry rather than constrain it. But a North Korean theft of this scale touches national security, sanctions enforcement and anti-money-laundering law, not just financial regulation — and those are areas where even a crypto-friendly administration has little room for leniency. Expect congressional hearings, fresh questions about how exchanges protect customer funds, and renewed pressure for rules on custody, audits and incident disclosure. In Europe and Asia, where regulators were already moving toward stricter exchange rules, the Binance hack will be cited as evidence that the work cannot wait.
What to Watch Next
- Withdrawals on Sunday: Whether Binance reopens withdrawals on 1 November as promised, and whether they operate without limits or delays, will be the first real test of its pledge to users.
- The remaining 10 per cent: How long it takes Binance to source the less liquid tokens it still needs to buy, and whether the cost of doing so grows as the market reacts.
- The full proof of reserves: The zero-knowledge proof due by Tuesday 3 November, and whether independent analysts find the backing it claims for the ten listed tokens.
- The laundering trail: What the FBI, the Secret Service and blockchain analytics firms uncover about how the stolen funds were converted into ether and moved, and whether any of it can be seized.
- Regulatory reaction: Whether US lawmakers and regulators respond with hearings or new rules on exchange custody and security, and how other major exchanges answer questions about their own defences.
Sources
- Reuters, “Binance Replenishes 90% of $6.3 Billion Losses After Major Hack”, via Global Banking & Finance Review, 31 October 2026
- New York Post, “Binance has already refunded 90% of the $6.3 billion stolen by North Korean hackers”, 31 October 2026
- Newsmax, “FBI: North Korea Behind $6 Billion-Plus Binance Crypto Heist”, 31 October 2026
- US Brief, “Binance says 90% of $6.3 billion hack covered; withdrawals due Sunday”, 31 October 2026
- Bitcoin.com, “Trump Speaks on $6.3B Binance Hack as FBI Confirms North Korea”, 31 October 2026

About the Author — advmannan1
Related Articles
OPEC+ Agrees in Principle to Hold December Oil Output Steady as Brent Nears Six-Month Highs
Seven core OPEC+ producers have agreed in principle to keep December oil output targets unchanged at Sunday's meeting,…
Gold Crashes to One-Year Low Below $3,900 as Silver Breaks $50 in a Brutal October for Precious Metals
Gold fell to its lowest in a year on Friday as rising oil prices hardened bets on another…
Volkswagen Posts €5.82 Billion Quarterly Loss — Its Worst Since Dieselgate — as Electric Golf Work Is Suspended
Volkswagen reported a €5.82 billion third-quarter loss, its worst since the Dieselgate scandal, and suspended work on the…