
Italy Fines Meta €805 Million for Reading Android Users’ Photo Galleries Without Consent

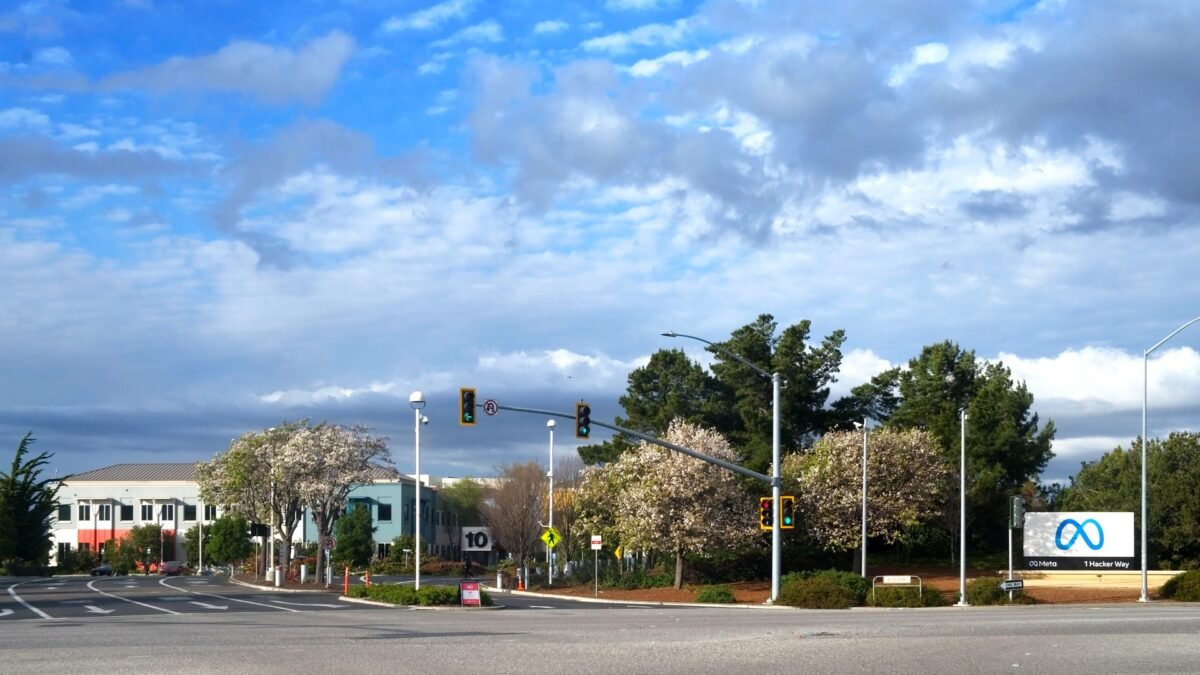
Italy has fined Meta €805 million after finding that the Facebook app on Android phones reached into the photo galleries of about 20 million Italian users without their specific consent, in one of the largest penalties ever imposed by an Italian authority on a technology company.
The fine, announced in Rome on Saturday 14 November 2026 by the Garante per la protezione dei dati personali, Italy’s data protection authority, is worth about $887 million, or £670 million, according to Reuters and the BBC. It is the second major penalty against Meta in less than a month, after a judge in New Mexico ordered the company in late October to pay $25 billion over its handling of user data.
At the centre of the Italian case is a Facebook feature that suggests photographs and videos from a phone’s gallery as ideas for posts while the user is browsing the app. The feature, called “Get suggestions from gallery when browsing Facebook”, has been available since 2023 and was switched on by default. According to the Garante, the Facebook app used it to access photographs, videos and the information attached to them stored on Italian users’ smartphones “without specific consent and without informing them”.
Meta has said it will appeal. A company spokesperson said Meta strongly disagreed with the regulator’s assessment of the facts and the application of the law, and called the fine “disproportionate”, according to Reuters.
What the regulator found
The Garante’s investigation began in July 2025, after a complaint from the Centro Tutela Consumatori Utenti, the consumer protection centre in Bolzano, in northern Italy. The authority carried out its own technical analysis of how the Facebook app behaved, and its findings, published in its official statement on Saturday, describe a permission system that gave the app far more access than users understood.
According to the Garante, gallery access was requested through a single authorisation that covered the whole app and several different functions with different needs. The notice shown to users before they granted it was generic, framed as enabling other features, and did not make clear that agreeing would also switch on gallery suggestions. The feature was then active by default, so many people were using it without ever making an active choice to do so.
The regulator said that once that broad permission was granted, the app could read a person’s entire photo archive, usually permanently, and neither the user nor the regulator could check what was actually being used. The findings concern improper access to the material, not a claim that Facebook copied every photograph from users’ phones or made private material public.
The case covers about 20 million Android users in Italy, according to the authority. The Garante said the practice breached Article 122 of Italy’s Privacy Code, the provision that implements Europe’s ePrivacy rules and protects information held on a person’s own device. The authority described the smartphone as part of a person’s private sphere, and said that any access to the information it contains requires free and informed consent, regardless of whether the data is transmitted elsewhere or whether any harm can be shown.
That framing matters. The ruling does not rest on proving that photographs were shared, sold or misused. It rests on the act of access itself. Under the rule the Garante applied, opening a private photo archive without a clear, specific yes is the violation, even if nothing further happens to the material.
The 60-day order
Alongside the fine, the Garante ordered Meta to redesign how the feature asks for permission, within 60 days. The company must ask for consent through a separate, specific request that explains clearly what the feature does, that it needs access to the gallery, and how to switch it off. The feature must be kept off by default, including for people who have already granted permission under the old system.
If the deadline passes without compliance, the feature cannot be activated for users who have not given valid consent. Meta must also report to the Garante within 30 days on the initiatives it has started, and within 90 days on the measures it has adopted.
The order reaches beyond a simple settings change. Because it applies even to users who already consented, Meta must go back to roughly 20 million people and ask again, this time with a clear explanation. The regulator’s message, in effect, is that a permission collected under a vague prompt does not count, and that the company cannot rely on it going forward.
In setting the size of the fine, the Garante said it took into account the high number of people affected, the fact that the practice was still continuing for people who had not updated the app and for those who had already given their consent, a previous decision against the company in 2019, and what it described as Meta’s lack of cooperation during the investigation. It also noted as a mitigating factor the changes Meta introduced after the complaint, though it judged those changes late and limited to people who update the app.
The €805 million figure works out at about 0.47 per cent of the group’s worldwide turnover, according to the authority. Meta reported 2025 turnover of $201 billion and a net profit of $60.5 billion, according to figures cited in coverage of the decision.
Meta’s response
Meta has rejected the regulator’s conclusions. “We strongly disagree with the assessment of the facts and the application of the law by the Garante and consider the amount of the fine disproportionate,” the company said in a statement reported by the Italian broadcaster Sky TG24. A spokesperson told the BBC that the regulator’s assessment of the facts, its interpretation of the law and the size of the penalty were disproportionate, and the company confirmed it intends to appeal.
Meta has maintained that the feature was designed to make it easier for users to share photographs and videos on Facebook, and that it only works after a device-level permission has been granted. The company also argued during the proceedings that the case should have been handled by Ireland’s regulator, where Meta has its European base. The Garante rejected that objection, on the grounds that the ePrivacy rules do not use the one-stop-shop system that applies to other data protection cases.
The appeal will run alongside the 60-day compliance clock, so the default setting on the Facebook app in Italy could change before the appeal is resolved. The full text of the Garante’s decision had not yet been published on its website by Saturday evening, according to reports, so the detailed reasoning behind the ruling was not yet available.
Why Rome, not Dublin
The jurisdictional point is one of the most consequential parts of the ruling, and it is the reason the fine comes from Rome rather than Dublin. Under the EU’s General Data Protection Regulation, known as GDPR, enforcement against a company with its European headquarters in Ireland is normally led by Ireland’s Data Protection Commission, under the one-stop-shop mechanism. That system was designed to give companies a single regulator to deal with, but it has also been criticised for concentrating enforcement in Dublin and slowing decisions.
The Garante’s case, however, was brought under the ePrivacy rules rather than GDPR. The ePrivacy directive protects the confidentiality of communications and of information stored on a person’s device, and it does not provide for a one-stop-shop. The Italian authority therefore held that it was competent to act on its own, and Meta’s objection failed.
That distinction opens a door that other national regulators may now walk through. If ePrivacy can be used to challenge how apps access material stored on phones, then regulators in France, Germany, Spain and elsewhere could bring similar cases against the same kind of feature without waiting for Dublin. The ruling is, in that sense, a test of whether Europe’s enforcement against big technology companies can move faster when it is channelled through a different law.
It also matters because the conduct at issue is not unique to Italy. The gallery-suggestion feature is available to Facebook users in other countries, and the same default-on design and the same single-permission structure would have applied to them. The Garante’s decision binds Meta only in Italy, but its reasoning will be read closely by regulators and consumer groups across Europe.
The AI question left open
One question the investigation deliberately did not answer is whether the photographs and videos accessed through the feature were used to train artificial intelligence models. The Garante said the proceedings did not examine that possibility, and Meta has denied using content accessed in this way for AI training.
The authority reserved the right to look separately at a newer feature, launched in 2026, that processes gallery content in the cloud. That reservation is significant. If a future inquiry finds that gallery material was used to train AI systems, the consequences for Meta would be considerably more serious than a fine for improper access, and the case would touch on one of the most contested questions in technology regulation: how companies obtain the data on which their AI models are built.
For now, the ruling is about consent and access, not about what happened to the material afterwards. But the open question hangs over the case, and it is likely to be the first thing other regulators and campaigners ask about next.
A familiar pattern: Meta’s long list of fines
The Italian penalty is far from Meta’s first encounter with a major fine, and it is not even the largest the company has faced this year. According to a compilation of big technology fines verified through 13 November 2026, Meta has been fined roughly €2.89 billion under GDPR across eight fines of €50 million or more, seven of them from Ireland’s Data Protection Commission between September 2021 and December 2024, and one €60 million fine from France’s CNIL in December 2021. Meta accounts for about 58 per cent of all big technology GDPR fines since the regulation took effect in May 2018.
The largest single penalty was the €1.2 billion fine imposed by Ireland’s Data Protection Commission in May 2023 over the unlawful transfer of European users’ data to the United States. Meta is appealing that decision. Other fines include €265 million in November 2022 after data from 533 million people was leaked from Facebook, and €91 million in September 2024 over the inadvertent storage of some users’ passwords.
In April 2025, the European Commission fined Meta €200 million under the Digital Markets Act, finding that its “consent or pay” model, which asked users to pay for an ad-free service or accept personalised advertising, failed to provide an equivalent, less personalised alternative. The Italian fine is four times that amount, and sits below only the €1.2 billion Irish penalty among European fines against the company.
The New Mexico case, decided in late October, is larger still. A judge there ordered Meta to pay $25 billion after finding that the company had spent years misleading the state’s residents about how it handled Facebook user data. Meta called that order a “tax” on freedom of expression. The Italian fine is the second major penalty against the company in less than a month, and it arrives while the New Mexico case is still fresh in investors’ minds.
Taken together, the fines tell a story about a company that has repeatedly been found to have taken more from users than the law allows, and that has repeatedly argued that its interpretation of the rules was reasonable. The amounts keep growing, but so far they have not changed the underlying business. Meta’s 2025 turnover of $201 billion puts the €805 million fine in perspective: it is about 0.47 per cent of annual revenue, or roughly a day and a half of sales.
What it means for Italian users
For the roughly 20 million Android users in Italy, the practical effect of the ruling will be a new, explicit choice the next time they open Facebook. Within 60 days, the gallery-suggestion feature must be off by default, and anyone who wants it must agree to it through a separate request that explains what it does.
That may sound like a small change, but it is the heart of the ruling. The Garante’s case is built on the idea that a person’s photo gallery is among the most personal material a phone holds: family photographs, children’s pictures, medical images, private moments that were never meant to be shared. A single broad permission, granted for one purpose and quietly extended to another, does not respect that. The regulator’s insistence on a separate, specific consent is an insistence that the choice to share must be made knowingly, feature by feature.
The ruling also carries a warning for users elsewhere. The same feature, the same default setting and the same permission structure exist in other countries. If the Garante’s reasoning is followed by other regulators, Facebook users across Europe could see the same new choice appearing on their phones in the coming months.
What happens next
Three clocks are now running. The first is the 60-day deadline for Meta to switch the feature off by default and introduce the separate consent request. The second is the appeal, which Meta has said it will file and which could take a year or more to resolve in the Italian courts. The third is the Garante’s reserved inquiry into the 2026 cloud-processing feature, which could produce a second decision on the same part of the app.
Meta must also report to the Garante within 30 days on what it has started to do, and within 90 days on the measures it has adopted. If the company fails to comply by the deadline, the feature cannot be activated for users who have not given valid consent, which would effectively switch it off for the Italian market.
The appeal will test whether the Garante’s reading of the ePrivacy rules holds up, and whether the size of the fine is justified. But even if the fine is reduced on appeal, the order to change the feature is likely to stand, and the precedent it sets for other regulators will remain. For Meta, the cost of the case is not only the €805 million. It is the prospect that the same argument, made in Rome, can now be made in every European capital.
Analysis: Why It Matters
The phone is the private sphere, and consent must be specific
The most important sentence in the Garante’s statement is not the size of the fine. It is the statement that the smartphone is part of a person’s private sphere, and that any access to the information it contains requires free and informed consent, regardless of whether the data is transmitted or any harm is shown. That is a deliberately broad principle, and it reaches far beyond one Facebook feature.
Modern phones hold more personal material than any filing cabinet or diary ever did. A photo gallery contains not only pictures a person chose to share, but pictures they chose not to share, pictures of their children, pictures taken in hospitals and bedrooms, pictures that were never meant to leave the device. The Garante’s ruling treats that archive as private by default, and access to it as something that must be asked for clearly and separately, not bundled into a general permission granted for other purposes.
If that principle is applied consistently, it will change how apps ask for access to phones. A single permission covering “the whole app and several functions” is the standard design of the app economy, and it is the design the Garante has now found unlawful, at least for gallery access. The ruling does not ban photo suggestions. It bans the shortcut of obtaining them through a permission that was never really about them.
Default-on is the business model on trial
The feature at the centre of the case was switched on by default. That detail is not incidental. It is the mechanism by which a feature reaches 20 million people without most of them ever choosing it. Defaults are powerful: most users never change them, and companies know it. A feature that is on by default will be used by millions; the same feature, off by default, will be used by a fraction of that number.
The Garante’s order to keep the feature off by default is therefore more than a technical fix. It is a direct challenge to a design philosophy that has served the technology industry well for two decades: make the data-collecting option the default, and let inertia do the rest. If regulators begin to require that data-access features start switched off, the economics of features like gallery suggestions change completely, because their value to the company depends on scale, and scale depends on defaults.
Meta’s defence, that the feature was designed to help people share photographs, is not obviously wrong. Photo suggestions are genuinely useful. But usefulness does not answer the question the Garante asked, which is whether users knew what they were agreeing to. A helpful feature that is switched on without a clear yes is still a feature that was switched on without a clear yes.
Rome just broke Dublin’s monopoly on Meta enforcement
For years, enforcement against Meta in Europe has run through Ireland, because the company’s European headquarters is there and GDPR’s one-stop-shop gives the Irish regulator the lead. That system has been criticised as slow and, by some consumer groups, as too close to the companies it regulates. Cases have taken years, and fines have often been reduced on appeal.
The Italian ruling shows there is another route. By bringing the case under the ePrivacy rules, which have no one-stop-shop, the Garante acted on its own and reached a decision in about 16 months, from the complaint in July 2025 to the announcement in November 2026. That is fast by European enforcement standards, and it will not have gone unnoticed in other capitals.
The significance is not only that Italy could act, but that other national regulators now have a template. If the same gallery feature is available in France, Germany or Spain, and the same permission structure applies there, there is nothing to stop those regulators from bringing their own cases under their own ePrivacy laws. The result could be a series of national fines, each smaller than a single EU-wide penalty, but together amounting to a far larger bill, and a far faster one.
The fine is small for Meta. The order is the real penalty
At about 0.47 per cent of worldwide turnover, the €805 million fine is, in financial terms, a rounding error for Meta. The company reported a net profit of $60.5 billion in 2025. The fine is roughly five days of profit. Investors barely reacted to the announcement, and the company’s share price is unlikely to be moved by a penalty of this size.
What matters more is the order. Forcing Meta to switch a feature off by default for 20 million users, and to ask each of them again for a separate, specific consent, strikes at the mechanism by which the feature generates value. If most users decline, or simply ignore the new prompt, the feature’s reach collapses, and with it the data it was collecting. That is a cost that does not appear on any balance sheet, but it is real.
The same logic applies to the reserved inquiry into the 2026 cloud-processing feature. If the Garante finds that gallery content processed in the cloud raises separate concerns, Meta could face a second order, and a second fine, on the same part of its app. The €805 million may be the first instalment, not the last.
Two fines in a month, and the cost of the old playbook
The Italian fine arrives less than a month after the $25 billion New Mexico order, and the two cases, different as they are, point in the same direction. In New Mexico, the finding was that Meta misled residents for a decade about how it handled their data. In Italy, the finding was that Meta took access to users’ photo galleries without properly informing them or obtaining specific consent. In both cases, the gap between what users understood and what the company did is the heart of the matter.
Meta’s response in both cases has been to disagree, to call the penalties disproportionate, and to appeal. That is the company’s right, and appeals are a normal part of the process. But the pattern is now hard to ignore: across Europe and the United States, regulators and courts are reaching the same conclusion, that the company’s approach to user consent has repeatedly fallen short of what the law requires.
The question for Meta is whether the playbook that built its business, ask broadly, default to on, explain later, can survive in a regulatory environment that now demands the opposite: ask specifically, default to off, explain first. The Italian ruling suggests it cannot, at least not in Europe. And the speed with which Rome acted suggests that other regulators will not wait long to test the same argument.
What to Watch Next
- The 60-day deadline: whether Meta switches the gallery-suggestion feature off by default for Italian Android users and introduces the separate consent request by mid-January 2027, and how many users choose to switch it back on.
- Meta’s appeal: when the company files its challenge in the Italian courts, and whether it argues the facts, the legal basis under Article 122, or the size of the fine.
- The Garante’s 30- and 90-day reports: what Meta tells the regulator about the initiatives it has started and the measures it has adopted, and whether the authority is satisfied.
- The cloud-processing inquiry: whether the Garante opens a separate investigation into the 2026 feature that processes gallery content in the cloud, and whether it examines the AI-training question it left out of this case.
- Copycat cases across Europe: whether regulators in France, Germany, Spain or elsewhere bring their own ePrivacy cases against the same Facebook feature.
- The full decision: publication of the Garante’s detailed reasoning, which will show exactly how it calculated the fine and how it weighed the mitigating changes Meta made after the complaint.
- The New Mexico case: whether Meta’s appeal there progresses alongside the Italian one, and whether the two penalties together change how investors and advertisers view the company’s regulatory risk.
Sources
- Garante per la protezione dei dati personali, “Facebook: il Garante Privacy sanziona Meta per 805 milioni di euro”, 14 November 2026, doc-web 10321080
- Reuters, “Italy fines Meta $887 million over Android users’ data access”, 14 November 2026
- BBC News (via World Right Now), “Meta hit with €805m Italian fine for reading phone galleries”, 14 November 2026
- AFP, “Italy fines Meta $880 mn over photo privacy: authority”, 14 November 2026
- PrivacyTerms.io, “Big Tech GDPR Fines 2026: EUR 5.0B Total Since 2018”, verified through 13 November 2026
- Mondaq / Legal 500, “The EDPB Flexes Its Muscles – Meta Fined In Excess Of €1.5bn”

About the Author — Abdul Mannan
Related Articles
US Wholesale Inflation Hits 6.5%, the Highest in Nearly Four Years, as the Fed Faces a December Rate Hike
US wholesale prices rose 6.5% over the year to October, the fastest in nearly four years, leaving the…
Wall Street Ends a Wild Week Lower as Nvidia’s Slide Deepens and Chip Stocks Plunge
Nvidia fell to a fresh 52-week low on Friday as chip stocks led Wall Street lower, yet the…
Poundland Wins Ten Days to Find a Buyer as MPs Accuse US Owner Gordon Brothers of Starving the Chain of Cash
Poundland has won ten more working days to find a buyer after filing a second notice of intention…