
Britain’s Cyber Chiefs Warn AI-Powered Ransomware Will Strike Critical Infrastructure by 2028

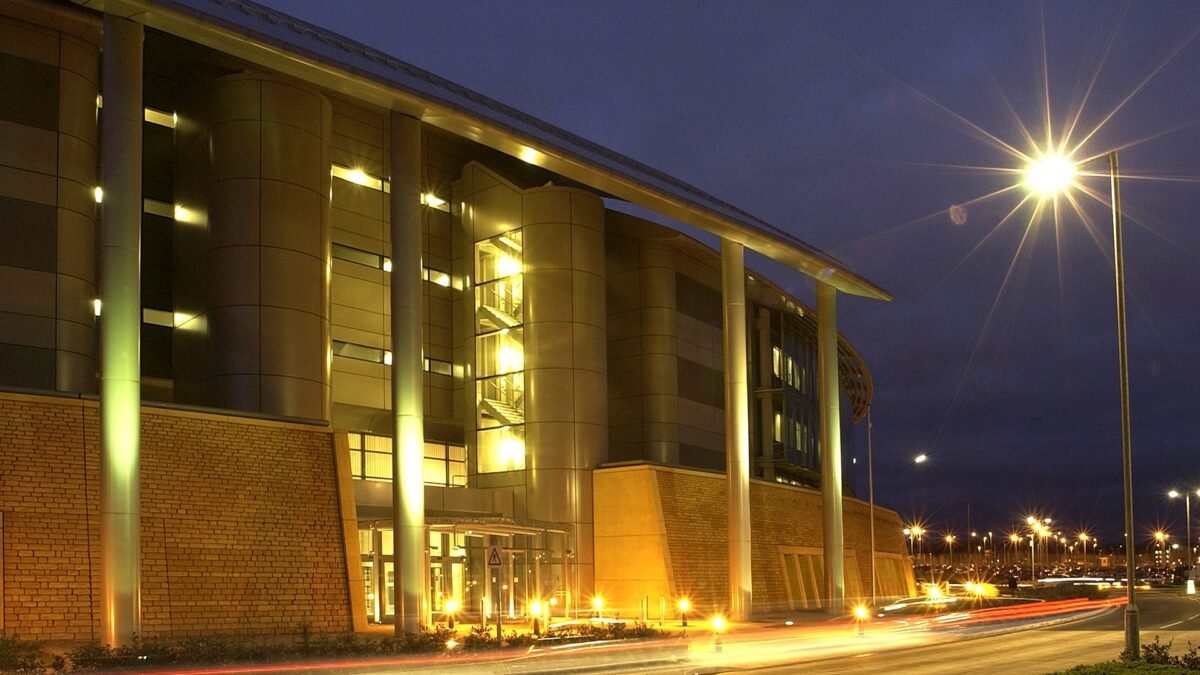
Britain should prepare for a ransomware attack powered by artificial intelligence to strike its critical national infrastructure within the next two years, the country’s cyber defence chief has warned, in the starkest official forecast yet of how AI is changing the threat to the systems that keep the lights on, the food on the shelves and hospitals running.
The National Cyber Security Centre (NCSC) said in its annual review, published on Tuesday, that it was “highly likely” AI-powered malware would be used in a ransomware attack on UK critical national infrastructure between now and 2028. Its chief executive, Richard Horne, told the launch event in London that the country faced “a real prospect of an unprecedented rise in the number of cyber incidents” in the coming months, according to Reuters.
The warning, carried in the NCSC’s State of the Cyber Nation report, covers power stations, airports, hospitals, water supplies, transport networks, food supply chains, defence systems and financial services — the sectors the UK classifies as critical national infrastructure. The agency, which sits within the GCHQ intelligence agency, said hostile states and criminal gangs alike would use AI to find weaknesses faster and attack at a scale that was previously impossible.
“But we must be clear that is not because AI has invented new ways to attack us, but because vulnerabilities that have been tolerated for far too long can now be discovered and exploited at a scale that was once unimaginable,” Horne said, in remarks reported by Reuters. “For decades, we have collectively got away with doing tech on the cheap.”
The NCSC judged that China was the country best placed to turn AI into a weapon against British infrastructure. “We know that China highly likely has the intent and is best positioned to use AI for operations against our critical national infrastructure and other strategic targets, with their activity representing the most sophisticated and sustained cyber challenge the UK faces,” Horne said, according to Reuters. He added that Russia was making sustained attempts to penetrate UK military networks, while Iran was carrying out malicious cyber operations globally, including against the UK and against individuals seen as a threat. Moscow, Beijing and Tehran have all repeatedly denied similar accusations in the past, Reuters noted.
The report also warned that Russia and China would routinely use AI in their cyber activity by 2028, and that the technology would increase the scale and efficiency of hostile operations during the same period. The NCSC’s assessment is a forecast, not a disclosure that the predicted attack has already happened — but it is the first time the agency has attached a specific ransomware scenario and a two-year horizon to the AI threat.
The warning landed on the same day the agency published figures showing a quieter year for the most serious attacks — a fall its chief insisted should not be mistaken for safety. Between September 2025 and August 2026, the NCSC received 1,831 reports of attacks on UK organisations, up from 1,727 a year earlier, according to Insurance Business, which covered the launch. It gave hands-on support in 337 cases, down from 429, and classed 80 as nationally significant, compared with 204 the year before — roughly one and a half a week against about four a week previously. The review itself said incident numbers rarely moved in a straight line and that past peaks were often caused by a handful of severe events. Its verdict on the country’s defences, quoted by Insurance Business, was blunt: “The UK’s cyber resilience is not yet where it should be.”
The agency managed more than 200 cyber incidents affecting UK critical infrastructure and its supporting ecosystem in the year to May 2026, according to the report, with around 75 per cent believed to be linked to state actors. The government estimates that malicious cyber activity costs UK organisations about £14.7 billion a year — roughly the size of the country’s entire cyber security sector, Insurance Business reported.
Horne’s message was aimed squarely at the boards and executives who decide how much their organisations spend on security. Leaders who kept putting off investment, he said, could end up explaining to investors, shareholders, employees, customers and suppliers why food was not on the shelves, the lights were not on and businesses had gone under. “We can be a nation where leaders of all organizations actively choose to invest with urgency and where all organizations make security and resilience a fundamental requirement, not an afterthought,” he said, according to Infosecurity Magazine. “The collective result would be a source of enduring national strength for us all.”
He described the country as standing at a “moment of choice”, opening his speech with the plot of the film Sliding Doors — the idea that seemingly small decisions can change the course of a future. “Ten years on from the NCSC’s formation, it is clear that our nation is living through a moment that, in hindsight, we will see as one of enormous consequence,” he said, according to the speech published by the NCSC. “A Sliding Doors moment.”
What the report found
The annual review, which covers the NCSC’s tenth year — 1 September 2025 to 31 August 2026 — paints a picture of an adversary that is getting faster rather than cleverer. Among large organisations, 88 per cent of the incidents the NCSC handled began in one of four familiar ways: exploiting a public-facing application, phishing, misusing a legitimate account, or exploiting remote access services, Insurance Business reported. The incident team has seen AI tools in use by attackers, but none of them has yet enabled a genuinely new type of attack.
The danger, the report argues, is speed and scale. AI can help attackers scout targets, find weaknesses in complex networks and write malicious code, according to the NCSC, and it expects AI models to uncover large numbers of previously unknown flaws in widely used software. The agency has told organisations to prepare for what it calls a “vulnerability patch wave” — a rush of urgent updates across the technology they rely on, hitting many organisations at once.
One concrete example is already in the wild. Researchers are increasingly seeing widespread abuse of ARTEX, an open-source, Chinese-made AI red-teaming platform, in attacks on the UK domain registrar 123 Reg, Microsoft 365 and other targets since its launch in July, according to The Register. The platform was originally built to help security researchers test defences; attackers have repurposed it.
The report also flags “shadow AI” — staff putting company data into unapproved AI tools, often on personal devices — as a growing risk that organisations will increasingly have to account for, Insurance Business reported.
In its pessimistic scenario for 2028, the NCSC envisages “a significant increase in the frequency and sophistication of cyberattacks worldwide”, with wider adoption of AI tools making it harder to work out who was behind an attack, The Register reported. China, the report says, “has likely played a role” in supplying those tools, “enabling them to hide their activities within the noise”. It also considers a further threat: an autonomous attacker operating beyond its human operator’s control. The NCSC said it was “a realistic possibility such an entity could self-replicate and conduct cyberattacks at will, with no apparent motivation or restraint”, according to The Register.
The state threat is not theoretical. The review calls China the most sophisticated and sustained cyber threat the UK faces, and Russia the most audacious, Insurance Business reported. It points to an attack in December 2025 on Poland’s energy grid, which the UK and the European Union attributed to a unit of Russia’s FSB intelligence service. Had it succeeded, around 500,000 people could have lost power. In August, hackers linked to Iran’s Islamic Revolutionary Guard Corps were understood to have shut down a “small” UK power station, according to New Civil Engineer, which reported the incident as understood rather than confirmed.
The NCSC’s own recent work underlines how much of the threat is still basic hygiene. In response to the PHP2Shell vulnerabilities, the agency issued 110,000 proactive notifications and Early Warning alerts to UK organisations, Horne said, according to Infosecurity Magazine. Its free Early Warning service, which alerts organisations to suspicious activity on their networks, now has 19,922 organisations signed up — a 52 per cent increase, Insurance Business reported.
The supermarket warning that came true
Horne’s speech came days after a real-world demonstration of the fragility he was describing. In early November, suspected cyber-attacks hit supermarket refrigeration systems in six European countries — Belgium, Luxembourg, Sweden, Ireland, the Netherlands and Estonia — forcing evaporators into defrost mode and pushing temperatures as high as 50°C, according to the BBC and the Associated Press. Around 40 Delhaize stores in Belgium and Luxembourg were affected, along with 15 Carrefour stores in Belgium, five Spar shops and a number of Swedish ICA and Coop stores. Millions of euros of food was thrown away.
It was the second wave of such attacks. On the night of 11–12 October, hackers remotely manipulated refrigeration systems at hundreds of supermarkets in France, including stores run by Carrefour, Intermarché, Coopérative U and Monoprix. France’s national cyber security agency, ANSSI, confirmed that controllers made by Danfoss, Copeland and Dixell had been compromised, and its CERT-FR alert recorded that attack campaigns were “probably still ongoing”. Around 700 of France’s roughly 10,000 supermarkets were affected, according to the French finance minister. In some stores, temperatures reached 80°C, and there were electrical fires.
The attackers exploited internet-connected controllers that had been left exposed online, in many cases running end-of-life hardware or outdated firmware — precisely the kind of “tech on the cheap” Horne condemned. Danfoss said most of the affected units in France were legacy or end-of-life hardware, including the AK-SC 355, phased out in 2016, and the AK-SM 800, which reached end-of-life in May 2021. Security researchers had warned about the flaws in advance: Claroty’s Team82 published three flaws in the AK-SM 800A, including an authentication bypass that derived a working login from the device date. No authority has publicly confirmed who was behind either wave, or whether the two waves were linked.
The NCSC said it was working with partners on the supermarket attacks and that there had been no incidents in the UK, according to earlier reporting. But Horne used the episode as his central example of what happens when basic weaknesses are left in place. Anthony Young, chief executive of the critical infrastructure security provider Bridewell, told Infosecurity Magazine that the NCSC’s two-year warning “feels generous”. “AI is already helping attackers, and vulnerability discovery is accelerating faster than many organizations can test and deploy patches. There is no time to wait when so many of the weaknesses attackers can exploit are already there,” he said, calling the supermarket attacks “a good example of this and an extension of the problems we have seen for years with internet-connected CCTV and heating or ventilation systems”.
The cost of getting it wrong
The review uses the 2025 cyber-attack on Jaguar Land Rover as its main example of the economic harm a single incident can cause. JLR reported about £196 million in direct costs from the attack, which halted production, and the review links the incident to UK economic growth of just 0.1 per cent in the third quarter of 2025, below forecasts, Insurance Business reported. Suppliers lost orders and payments while production stopped — the kind of knock-on damage that spreads far beyond the company that was hit.
The wider bill is far larger. The government estimates cyber-attacks cost UK organisations about £14.7 billion a year, a figure repeated in the review. Insurance Business noted that the figure was roughly the size of the UK’s entire cyber security sector, and that cyber insurance rates have been falling for nearly three years even as the underlying risk moves the other way.
The NCSC’s answer, repeated throughout the report and the speech, is to start with the basics and scale up from there. Take-up of its Cyber Essentials certification is still rising: 47,661 certificates were awarded in the 12 months to August, up 19.6 per cent, and Cyber Essentials Plus certificates rose 21.5 per cent to 15,646, Insurance Business reported. The government says certified organisations are 92 per cent less likely to make a claim on their cyber insurance, based on data from the insurer that provides the free cover bundled with certification.
At the launch event, Cyber Security Minister Baroness Lloyd announced a 75 per cent discount on Cyber Essentials certification for micro, small and medium-sized businesses, bringing the cost down to between £80 and £125 plus VAT, according to Infosecurity Magazine. More than 230 businesses have also signed up to the government’s Cyber Resilience Pledge, which allows participating organisations to refer small and medium-sized firms in their supply chains for free Cyber Essentials certification, with selected businesses also receiving support from a free cyber security adviser.
Britain’s answer: Cyber Shield, NERV and a new AI security centre
The government used the launch to set out a package of new investment in AI-driven cyber defence, much of it announced in last week’s Budget. It is putting £60 million into the first phase of a national Cyber Shield, including a £25 million Challenge Fund supporting UK AI and cyber security innovators, and £70 million into a new National Exposure and Real-Time Vulnerability (NERV) Centre, according to Infosecurity Magazine. The NERV Centre’s job will be to identify and maintain an ongoing understanding of vulnerabilities across critical infrastructure organisations and the wider economy, The Register reported.
Alongside those announcements, the government has committed £120 million to the AI Security Institute and the establishment of a new AI Cyber Security Centre of Excellence, run by the NCSC in Manchester, to provide world-leading AI security expertise within government. It has also committed £40 million to establishing a National Agentic Security Unit to monitor and respond to uncontrolled AI bots, alongside a further £24 million to strengthen public-sector cyber defences using advanced AI technology, Infosecurity Magazine reported.
Cyber Shield, an agentic cyber defence system first teased in July, is expected to be delivered in stages over the next five years, The Register reported. It will involve the NCSC providing defensive agents deployed by participating organisations with data that will strengthen national resilience to ongoing cyber threats. The NCSC will run the scheme alongside the Department for Digital, Culture, Media and Sport, but acknowledged that this kind of automated defensive activity currently sits outside many organisations’ risk tolerances — meaning it has a role to play in building trust in the system before adoption can go mainstream.
The NCSC is also exploring how AI could help defenders keep pace with attackers. Project DROMOS, launched by the Government Cyber Coordination Centre with the AI Security Institute and other departments, began earlier this year with a four-week pilot analysing government code repositories before expanding into selected operational environments, The Register reported. It has uncovered hundreds of potential security issues, including critical vulnerabilities.
The government also announced 14 new Software Security Ambassadors, including Fortinet, Thales, Capgemini and Zscaler, which will work with the government to promote secure software development and encourage wider adoption of its Software Security Code of Practice, Infosecurity Magazine reported.
On the legislative side, the Cyber Security and Resilience Bill is still going through Parliament. It would bring managed service providers and other sectors into regulation and give ministers new powers during national security crises, Insurance Business reported. The Association of British Insurers has backed the bill, citing nearly £200 million in cyber claims paid in a single year. A National Cyber Action Plan is also due to be announced soon, and the Government Cyber Action Plan is backed by more than £210 million of investment, according to the NCSC’s ministerial foreword.
Analysis: Why It Matters
1. The threat has flipped from “if” to “when” — and the NCSC has put a date on it
Cyber agencies rarely attach a deadline to a forecast, and rarer still to a specific scenario. The NCSC’s judgement — “highly likely” that AI-powered malware features in a ransomware attack on UK critical infrastructure by 2028 — is the closest thing to a dated prediction the agency has ever issued. That matters because it converts an abstract anxiety about AI into a planning horizon: two years to fix the weaknesses that are already known. Boards that treat cyber security as an IT line item now have a named risk, a named deadline and a named adversary in the official record. The question for every organisation that runs essential services is no longer whether AI will change the threat, but whether their own patching and monitoring can keep up with a machine that never sleeps.
2. AI is not inventing new attacks — it is industrialising old ones
Horne’s most important line was also his most counter-intuitive: AI has not invented new ways to attack. The NCSC’s own data supports him. Nearly nine in ten incidents at large organisations still start with one of four well-worn techniques — a vulnerable public-facing application, a phishing email, a misused legitimate account or an exposed remote-access service. What AI changes is the economics. A human attacker can probe a handful of targets; an AI system can scout thousands, test them for known flaws and write the exploit, all at once. The supermarket fridge attacks are the proof of concept: the flaws were known, the warnings were public, and the devices were still online and unpatched. The lesson is uncomfortable but simple — the next big incident is more likely to come through a door everyone already knew was open than through a novel zero-day nobody had seen.
3. China is named as the benchmark threat — and the attribution problem is getting worse
The report singles out China as the most sophisticated and sustained cyber threat Britain faces, and the only country the NCSC says is both likely to intend an AI attack on critical infrastructure and best placed to carry one out. That is a significant public judgement, and it sits alongside a warning that AI will make attribution harder: in the NCSC’s pessimistic 2028 scenario, China “has likely played a role” in supplying AI tools that let attackers hide “within the noise”. The implication is that the next serious incident may arrive with no clear fingerprint, which makes deterrence, diplomacy and retaliation all harder. It also raises the stakes of the autonomous-attacker scenario the report floats — an entity that could self-replicate and attack at will, with no apparent motivation, would leave governments unable to say who to blame, let alone how to respond.
4. The economics of defence are finally moving — but the gap is the story
The government is spending serious money: £60 million for Cyber Shield, £70 million for the NERV Centre, £120 million for the AI Security Institute, £40 million for the National Agentic Security Unit and £24 million for public-sector defences, plus a 75 per cent discount on Cyber Essentials for small businesses. That is a real commitment, and the Cyber Essentials numbers show the basics are spreading. But the NCSC itself warns of a widening gap between organisations that can afford modern, AI-assisted defences and those stuck with old systems — and the review’s own verdict is that the country’s resilience “is not yet where it should be”. The JLR attack showed that one company’s failure can shave national growth; the fridge attacks showed that the weakest link can be a controller in a supermarket basement. Money at the top of the system only helps if it reaches the bottom of the supply chain, where the devices are oldest and the budgets thinnest.
5. The warning is also a test of whether Britain learns from its own recent history
The NCSC’s tenth anniversary gives the report a reflective edge. A decade ago, the agency was created to professionalise the country’s cyber defences; a decade on, its chief is saying the fundamentals still are not in place. The “Sliding Doors” framing is deliberate: Horne is telling organisations that the choices they make now — patching, monitoring, refusing to connect things to the internet that do not need to be connected — will decide whether the next two years bring a manageable incident or a national disruption. The supermarket attacks, the JLR shutdown and the Poland grid attack are all recent, all documented and all preventable in the narrow sense. The question the report really asks is whether Britain’s institutions will act on a warning delivered in plain language, with a date attached, before the incident it predicts arrives.
What to Watch Next
- Whether any AI-powered ransomware incident hits UK critical infrastructure before 2028 — and whether the NCSC’s forecast proves early, on time or optimistic.
- The passage of the Cyber Security and Resilience Bill through Parliament, and whether it brings managed service providers and other sectors under regulation as planned.
- The rollout of Cyber Shield and the NERV Centre, and whether organisations trust agentic defensive systems enough to adopt them at scale.
- Attribution of the European supermarket refrigeration attacks — and whether investigators establish a link between the October and November waves, or identify who was behind them.
- The NCSC’s promised “vulnerability patch wave” — whether AI-driven discovery of flaws in widely used software forces a rush of urgent updates, and whether organisations can patch fast enough to keep up.
Sources
- NCSC Annual Review 2026 — Foreword by Richard Horne, CEO, NCSC
- Richard Horne’s speech at the NCSC Annual Review 2026 launch
- Reuters — UK must expect AI-powered attack on critical infrastructure within two years, report says
- Infosecurity Magazine — NCSC Chief Warns of AI Ransomware Threat to UK Critical Infrastructure
- The Register — Britain on notice: AI-powered ransomware attacks to arrive by 2028

About the Author — Abdul Mannan
Related Articles
AI Chatbots Gave Voters Wrong Election Answers in Nearly 40% of Tests as Americans Vote in the Midterms
A Forum AI study found almost 40% of chatbot answers to election questions contained a factual error —…
OpenAI Signs Four Deals in Abu Dhabi as ADNOC Becomes First Energy Company to Deploy Frontier AI
OpenAI chief executive Sam Altman signed four agreements in Abu Dhabi on Monday, led by a multi-year deal…
Apple Intelligence Finally Reaches China in December as Alibaba’s Qwen Powers Siri, Writing Tools and Visual Intelligence
Apple has confirmed that its AI features will reach iPhone users in mainland China in December, powered by…